SOC 2 (System and Organization Controls 2) is an auditor's opinion that your stated controls were designed correctly and operated consistently across a review window, typically three to 12 months. The controls are measured against the 2017 AICPA Trust Services Criteria, and for a software company most of the evidence an auditor samples is engineering evidence:
- Who reviewed each change
- Who authorized each deployment
- Which vulnerabilities were found, and how fast they were fixed
- Who had access to what
Most organizations assemble that evidence from a source control tool, a CI system, several scanners, a ticketing system, and a compliance vendor that screen-scrapes all of them. Every seam between those tools is a place where evidence can go missing during fieldwork.
This guide explains how GitLab closes those seams. It covers where each SOC 2 criterion lands in GitLab, which scanners back which criteria, where GitLab Duo speeds up the work, and which obligations GitLab does not cover.
How GitLab assists SOC 2 adherence
GitLab supports SOC 2 adherence in three ways.
Controls are enforced above the project
A custom compliance framework marks which projects are in scope, injects a compliance pipeline they cannot remove, and carries the requirements each project is measured against.
Security policies live in a separately permissioned policy project, so a developer with the Maintainer role cannot disable the control that governs them. GitLab offers four policy types: scan execution, merge request approval, pipeline execution, and vulnerability management.
A SOC 2 framework template ships with its requirements and controls already mapped, so you configure the framework instead of building it from scratch.
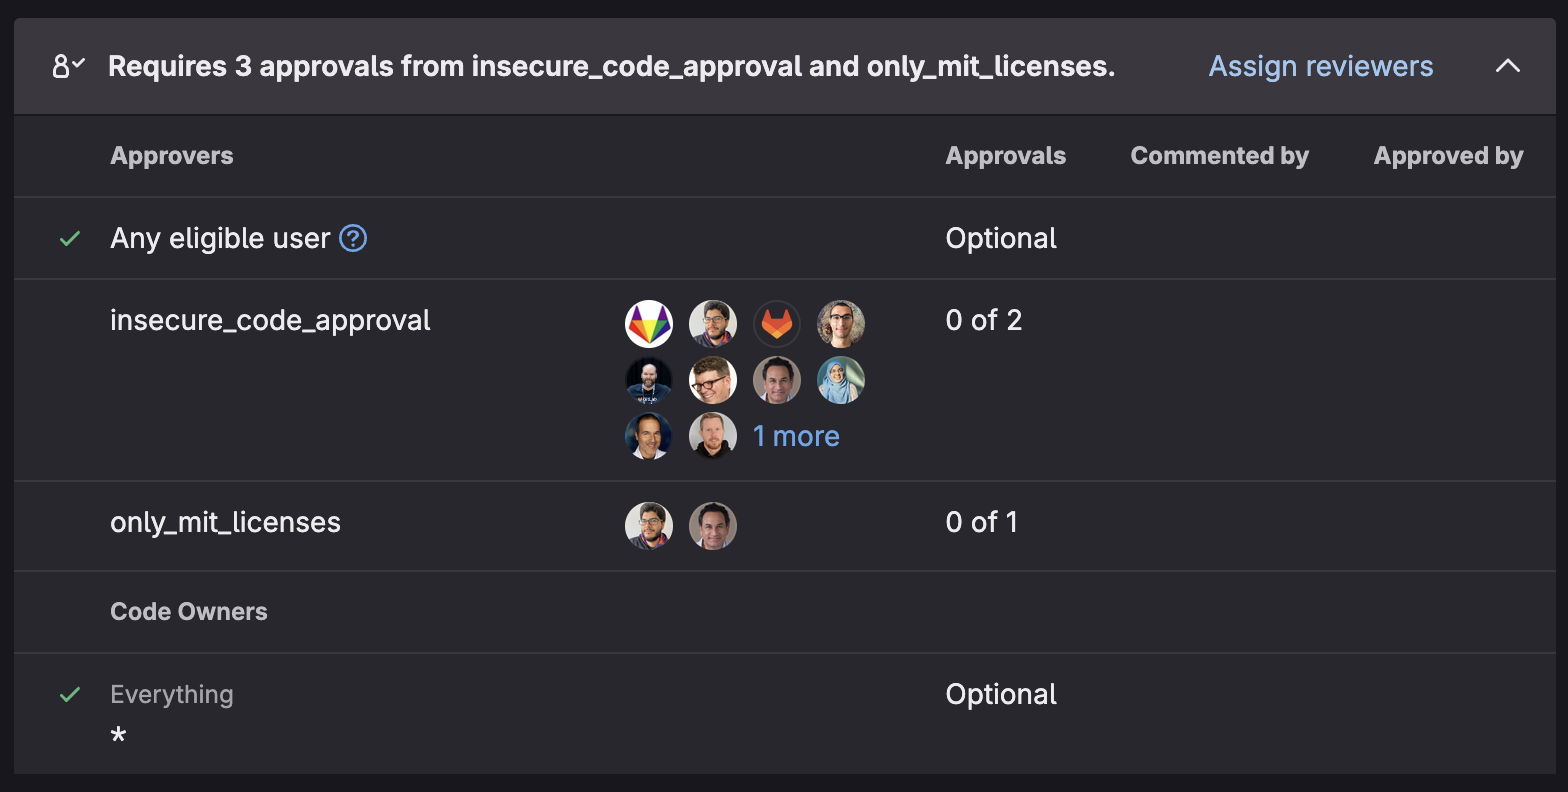
Evidence is a by-product, not a project
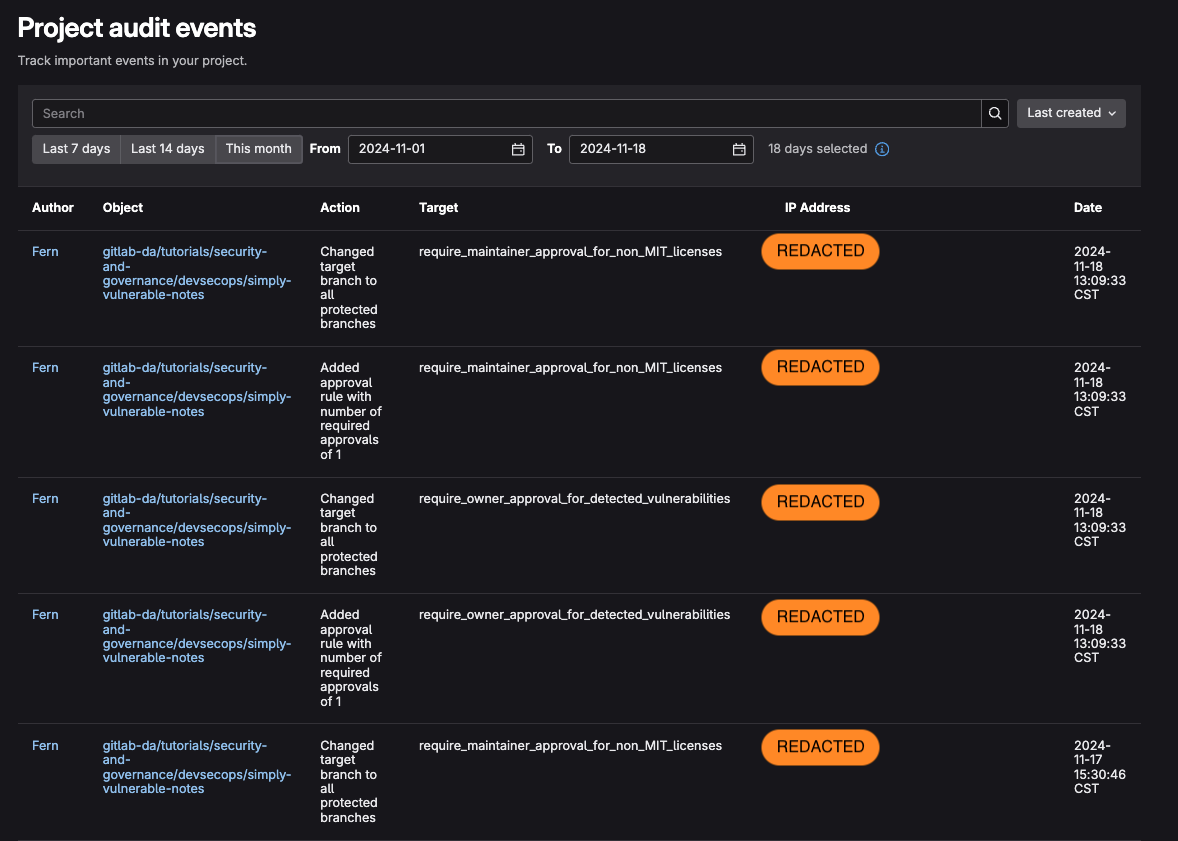
Normal engineering activity generates merge request approvals, pipeline results, scan reports, vulnerability state changes, and audit events. Each of these is attributable, timestamped, and tamper-evident by default, so audit preparation means exporting evidence that already exists instead of reconstructing it.
Drift is visible while you can still fix it
GitLab re-evaluates adherence whenever a framework changes, and again every 12 hours. The security inventory shows where scanner coverage is actually missing.
The most common cause of a Type II exception is a project created mid-window without the framework applied. With these checks, that gap surfaces within hours instead of at the next audit.
As a result, the criteria with the heaviest sampling burden are answered from one system, with one link per sampled change. Those criteria are CC6 (access control), CC7 (vulnerability management), and CC8 (change management).
Where the criteria land
The table below maps each SOC 2 Common Criterion to the GitLab capability that satisfies it and to the evidence artifact you hand to the auditor.
| SOC 2 criterion | GitLab capability | Evidence artifact |
|---|---|---|
| CC3.2 Risk identification | Security inventory, dependency list | Inventory export, group vulnerability report |
| CC5.2, CC5.3 Control deployment | Compliance pipelines, scan execution policies in a separate policy project | Policy YAML under version control |
| CC6.1–6.3 Access control | SAML/SCIM, enforced 2FA, custom roles, expiring membership, Security Manager role | Members export with roles and expiry, access audit events |
| CC6.6–6.8 Credentials and integrity | Secret Detection with push protection, signed commits, protected branches | Findings, branch protection settings, signature status |
| CC7.1 Vulnerability detection | The full scanner suite (see Scanner coverage) | Vulnerability report with severity and detection date |
| CC7.2 Anomaly monitoring | Audit event streaming to a SIEM | SIEM ingestion records |
| CC7.3–7.5 Response and remediation | Incident management, vulnerability workflow states with SLA | Incident timelines, state changes with actor and timestamp |
| CC8.1 Change management | Merge request approval policies, no self-approval, protected branches | One merge request link showing author, approvers, pipeline, and merge time |
| CC9.2 Supply chain | Dependency Scanning, license approval policy, CycloneDX SBOM | SBOM per project, license violations |
Criteria are defined in the 2017 AICPA Trust Services Criteria.
What this means: GitLab already produces the artifacts for CC6, CC7, and CC8, the criteria that dominate an engineering SOC 2 sample. Your work is to enforce them above the project level, so the artifacts appear by default instead of by convention.
Access control (CC6.1–6.3)
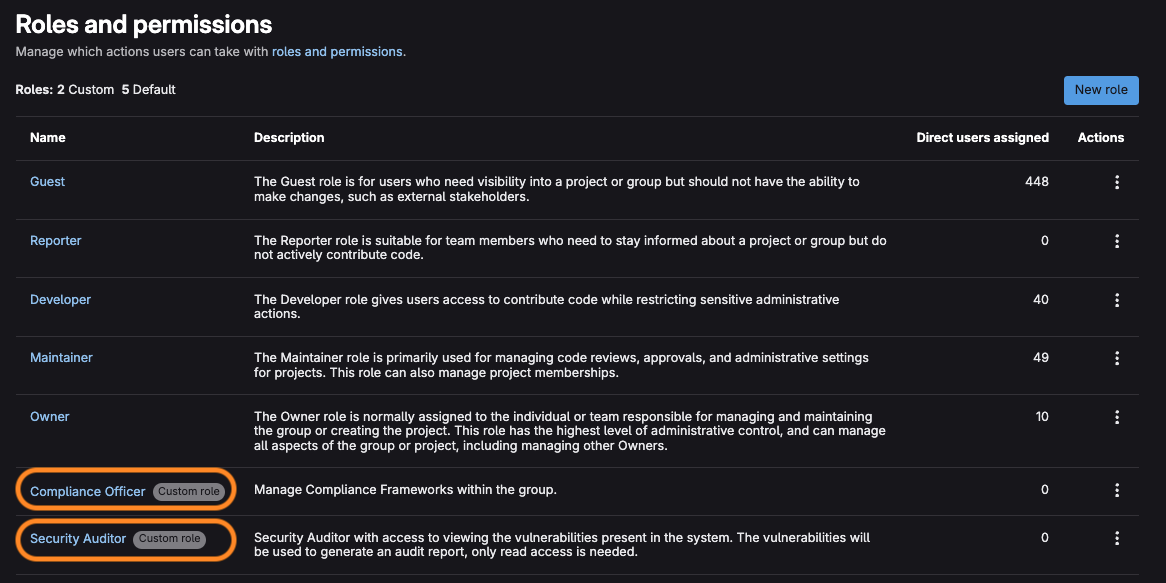
Custom roles let you grant fine-grained permissions beyond the default roles and follow the principle of least privilege. Pair them with SAML/SCIM provisioning, enforced two-factor authentication, and membership expiry dates so that access is revoked on schedule. The members export and access audit events become your CC6 evidence.
Credentials and integrity (CC6.6–6.8)
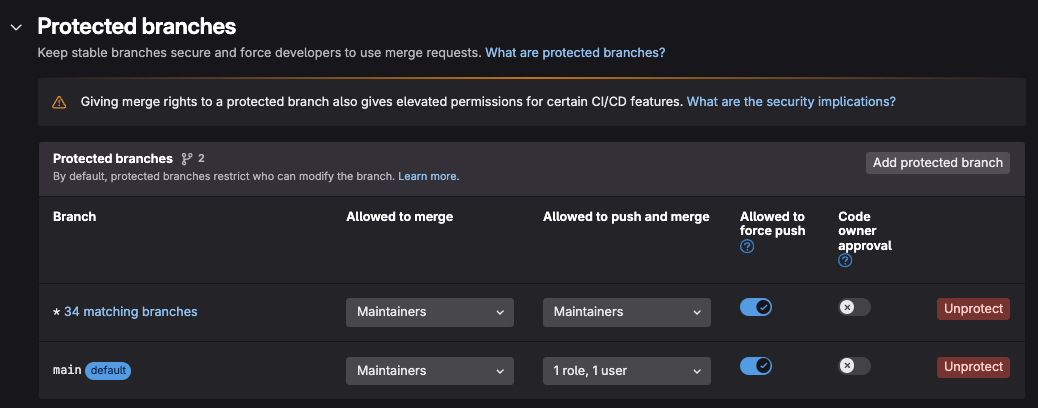
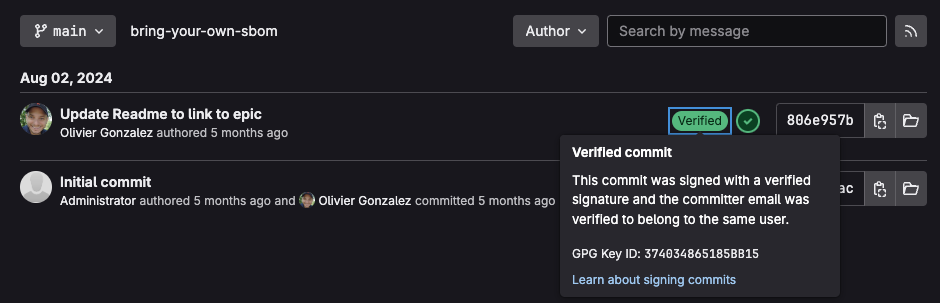
Protected branches and Code Owners control who can change which code. Signed commits prove each change came from the person it claims to come from. Secret Detection with push protection blocks a credential before it ever reaches the repository.
Anomaly monitoring (CC7.2)
Audit events record changes across groups and projects, with the actor and timestamp of each one. Streaming them to your SIEM puts GitLab activity alongside the rest of your monitoring, and the ingestion records serve as CC7.2 evidence.
Change management (CC8.1)
For a sampled change, the auditor wants to see who wrote it, who approved it, that the pipeline passed, and when it merged. In GitLab, that is a single merge request link. Merge request approval policies, a ban on self-approval, and protected branches ensure that every change follows the same path.
Scanner coverage
No single scanner satisfies CC7.1, because it requires coverage of code, dependencies, containers, infrastructure, and runtime together. The table below shows which criteria each scanner supports and how its results are enforced.
| Scanner | Primary criteria | Enforcement mechanism |
|---|---|---|
| SAST / Advanced SAST | CC7.1 | Scan execution policy; merge request approval policy on new critical and high findings |
| Business logic scanning (beta) | CC6.1, CC7.1 | Scan profile runs on every merge request; full-repository scans feed the vulnerability report |
| Secret Detection | CC6.1, CC6.6, CC6.7 | Pre-receive push protection blocks the commit |
| Dependency Scanning | CC7.1, CC9.2 | Scan execution policy; merge request approval gated on severity |
| License approval policy | CC9.2 | Blocks merge on a disallowed license |
| Container Scanning | CC7.1, CC6.8, CC9.2 | Scan execution policy; scheduled registry rescans |
| IaC Scanning | CC6.6, CC6.8, CC7.1 | Scan execution policy on infrastructure repositories |
| DAST / API security testing | CC7.1, CC6.1 | Scheduled policy against staging |
| Coverage-guided fuzzing | CC7.1 | Pipeline job in the compliance pipeline |
| SBOM / dependency list | CC9.2, CC3.2 | Generated by every compliant pipeline |
| Operational container scanning | CC7.1, CC7.2 | Agent-based scheduled scan |
What this means: The enforcement column is the part auditors actually test. A scan that runs but blocks nothing is telemetry, not a control.
That is why scanners should be enforced through a scan execution policy in the policy project instead of through an include: that each project can edit or remove. For example:
      scan_execution_policy:
  - name: SOC 2 baseline scans
    description: Run SAST, Secret Detection, and Dependency Scanning on every pipeline
    enabled: true
    rules:
      - type: pipeline
        branches:
          - "*"
    actions:
      - scan: sast
      - scan: secret_detection
      - scan: dependency_scanning
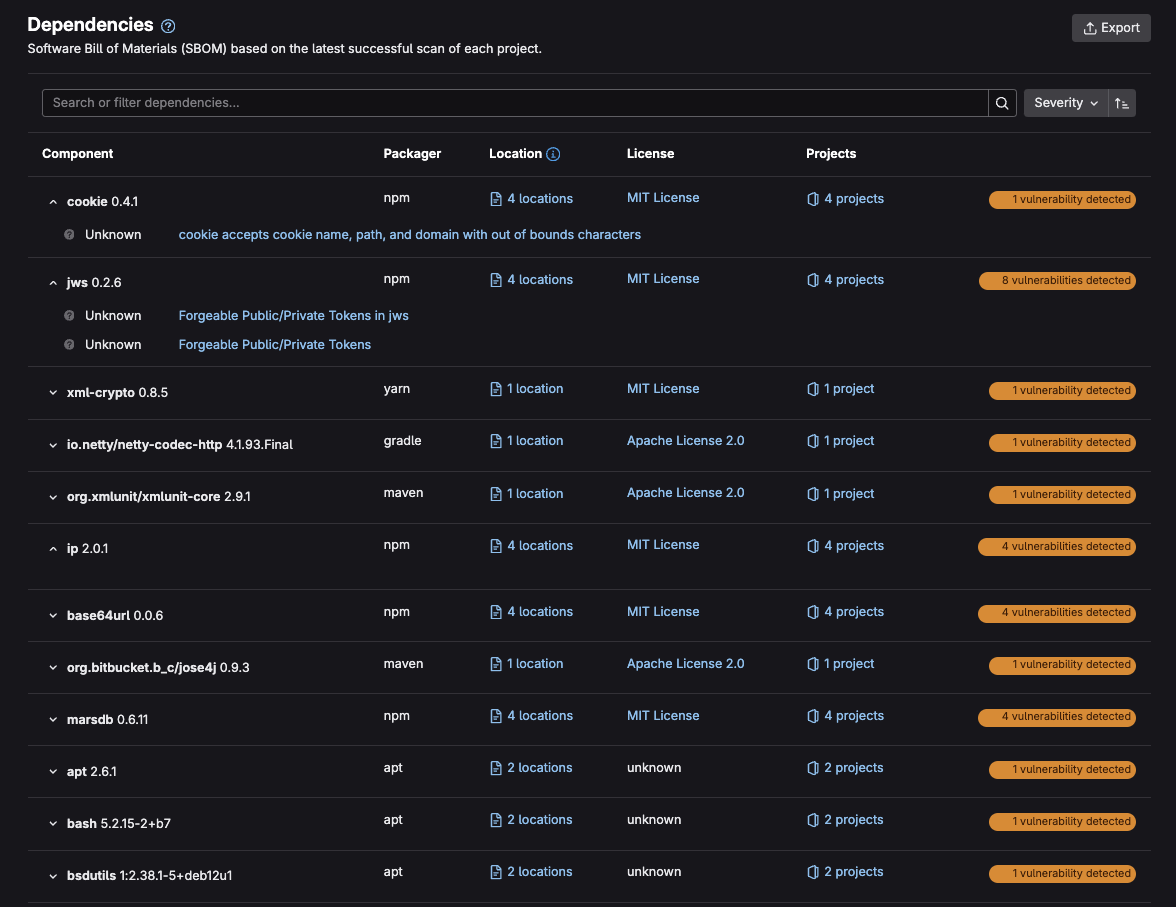
Once a pipeline runs, findings appear directly in the merge request, and a merge request approval policy can require security sign-off before vulnerable code merges.
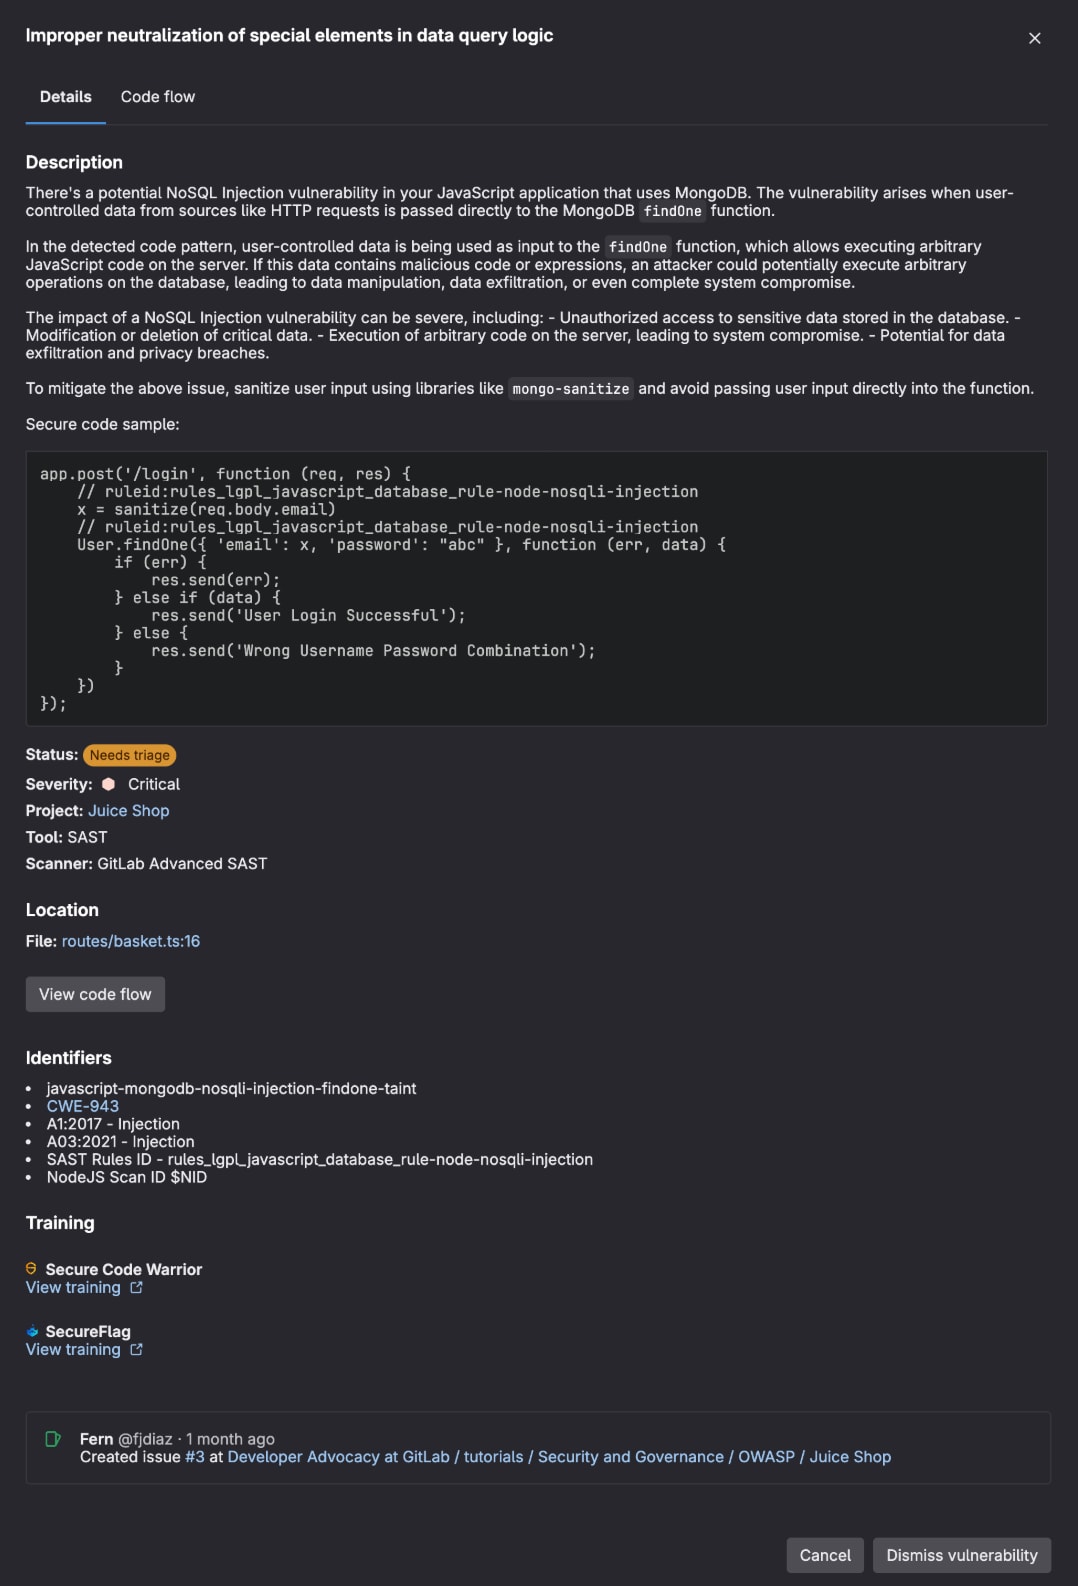
Every compliant pipeline also generates a software bill of materials (SBOM), which you can review at the group level. This gives you CC9.2 and CC3.2 evidence without a separate tool.
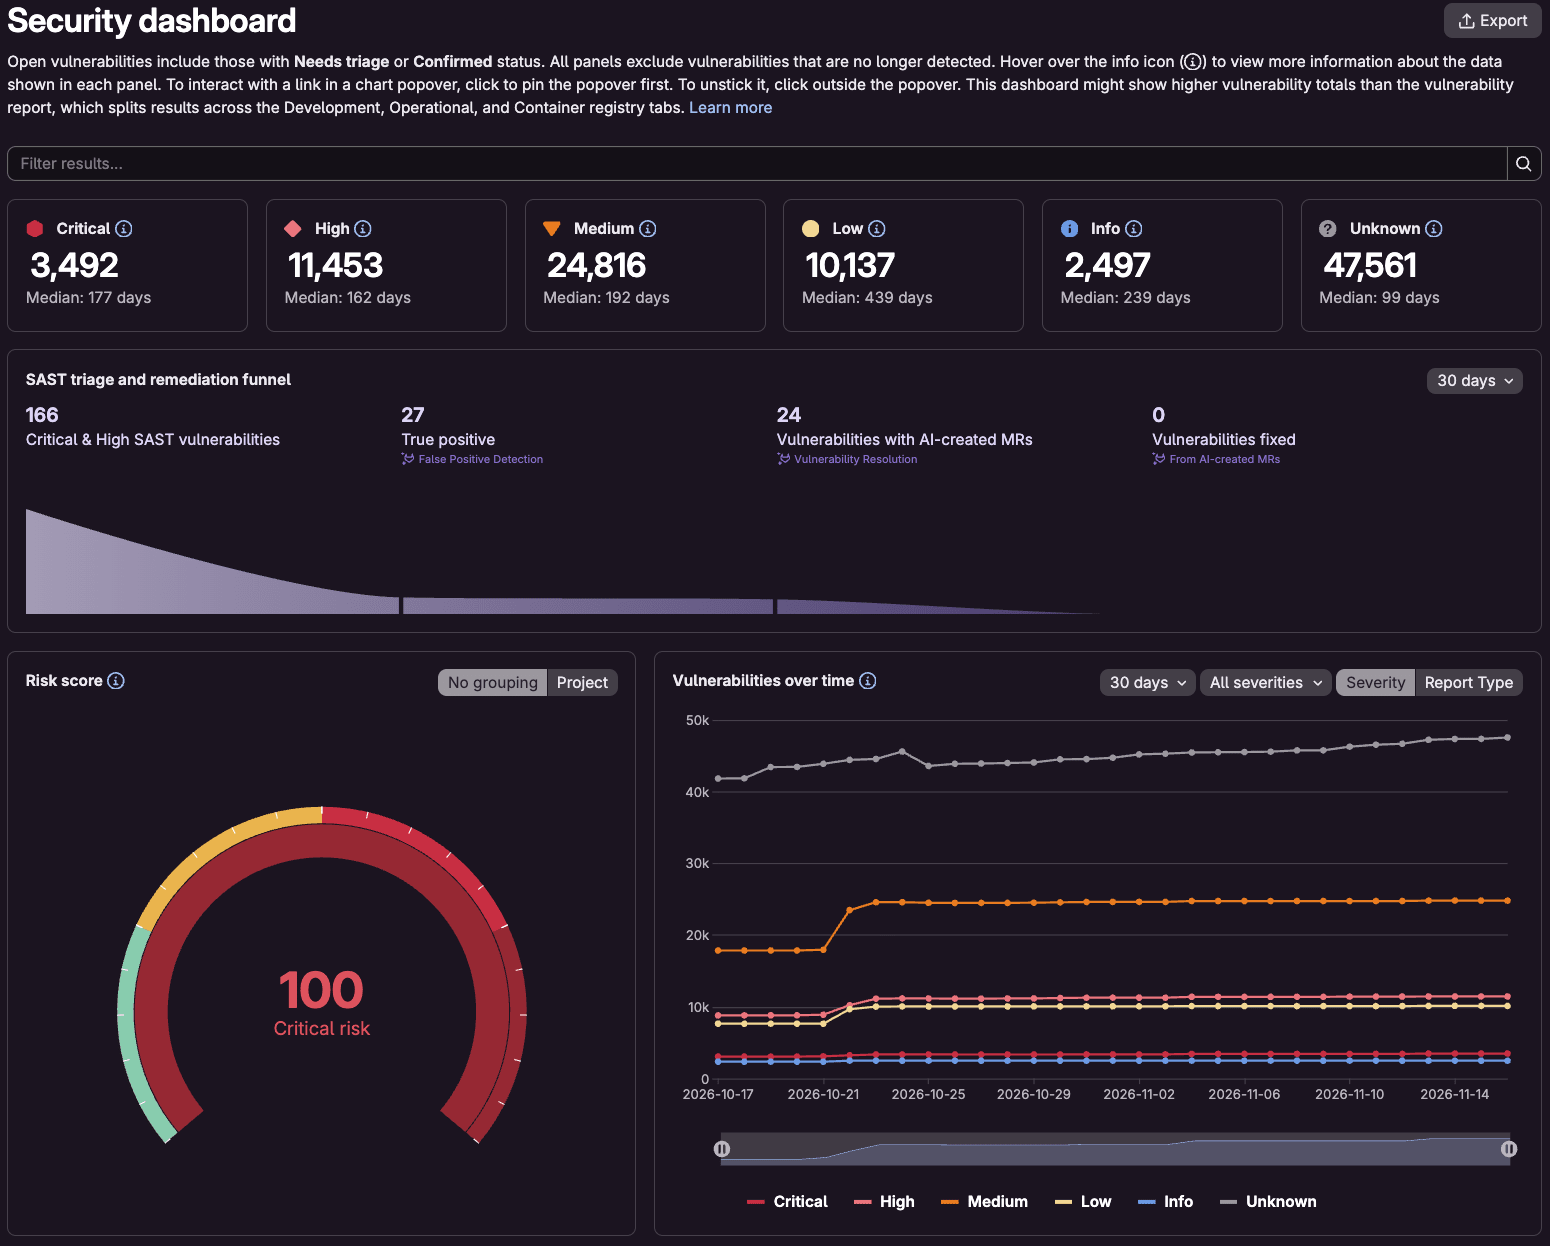
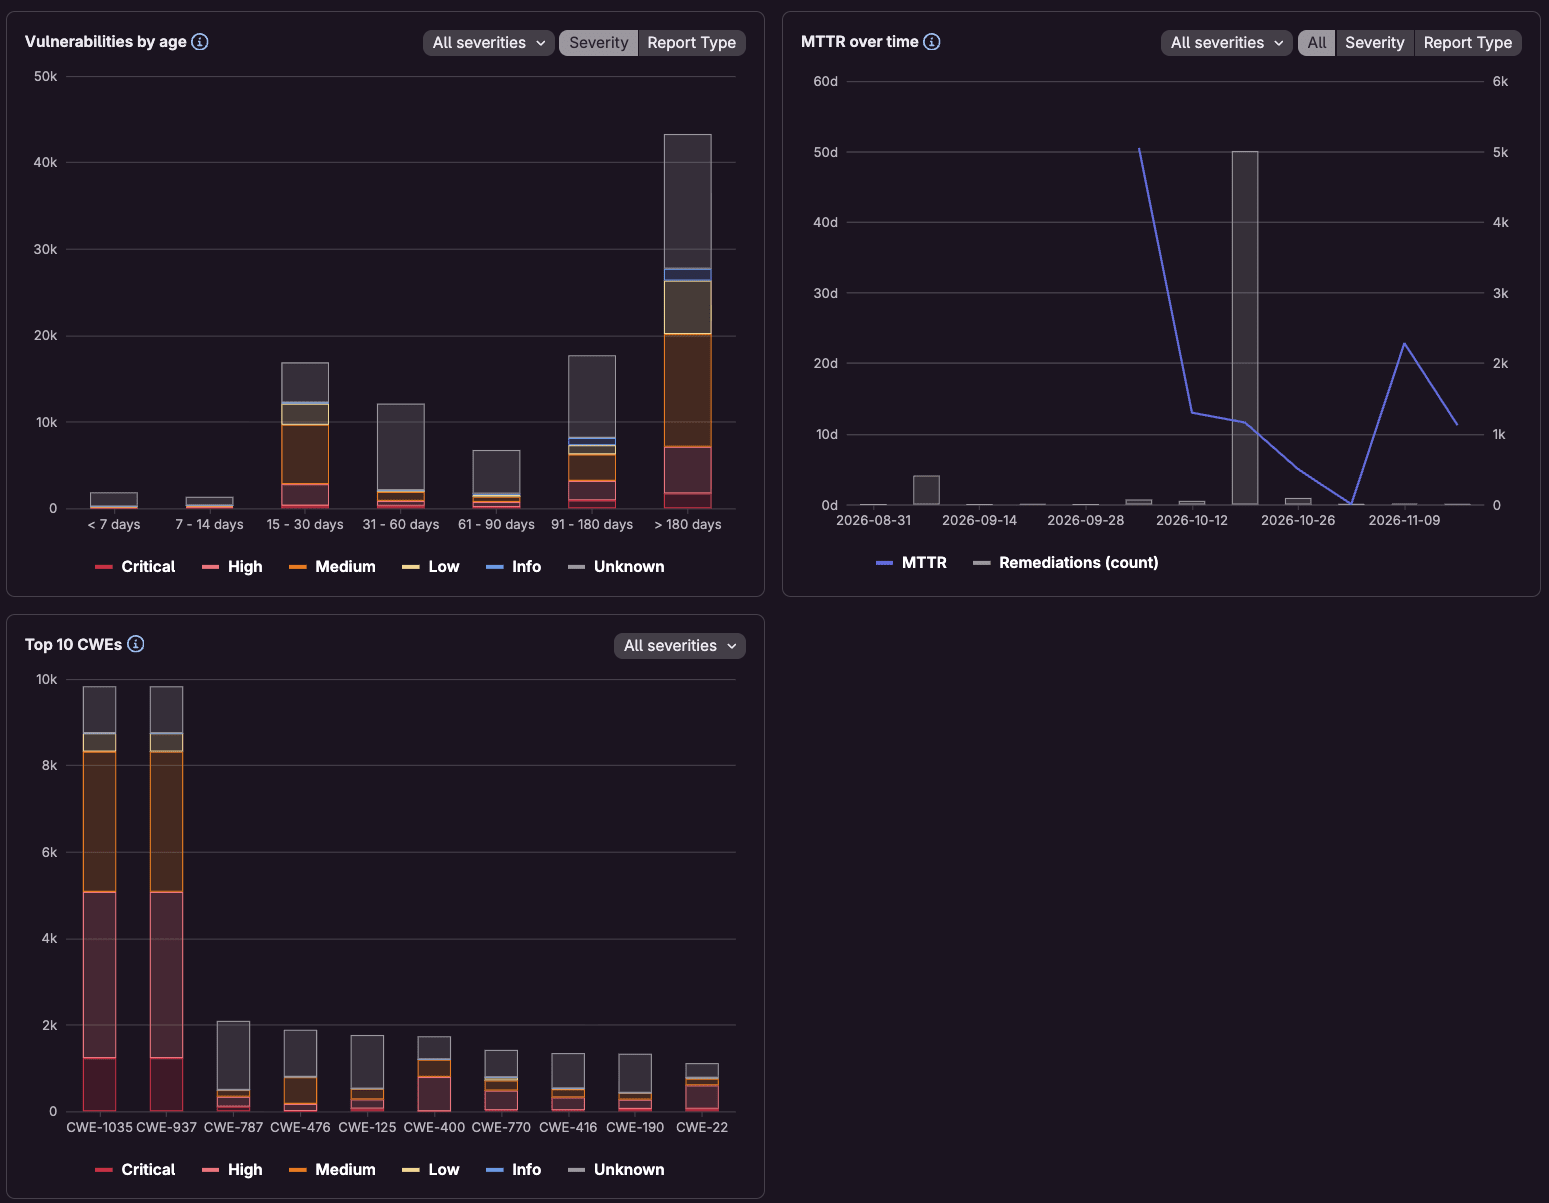
The security dashboard aggregates results from every scanner across projects, so you can track vulnerability trends over the full audit window.
Where AI helps
GitLab Duo shortens the slowest steps in the controls above: triage, remediation, and evidence summaries.
| Duo capability | What it shortens | Criterion |
|---|---|---|
| Vulnerability Explanation | Documents each triage decision with reasoning, not just a severity label | CC7.1, CC7.4 |
| Vulnerability Resolution | Time to remediate against your stated SLA | CC7.5 |
| Secret false positive detection | Separates real credential exposure from noise | CC6.6, CC7.1 |
| Business logic scanning | Finds broken authorization, missing access checks, and mass assignment that pattern-based scanners miss | CC6.1, CC7.1 |
| Duo Code Review | Adds review feedback beneath human approval, never in place of it | CC8.1 |
| Duo Security Analyst agent | Risk-based triage and audit-ready evidence summaries | CC3.2, CC7.1 |
| Session-based AI audit trail | Proves what agents did, streamed to the same SIEM | CC7.2 |
What this means: Duo accelerates controls; it does not replace them. Auditors will ask how AI is governed, and that answer matters as much as the speed gains:
- Agents act within the permissions of the user who requested them.
- Agent-authored code clears the same gates as human-authored code.
- Every agent session is logged.
A human remains accountable for every merge.
What GitLab does not cover
SOC 2 spans the whole organization, not just engineering. These obligations stay outside GitLab:
| Obligation | Where it gets done |
|---|---|
| HR controls, security training, background checks | HRIS and training platform |
| Device management, endpoint protection | MDM vendor |
| Physical and environmental security | Your cloud provider's own SOC 2 report |
| Production cloud IAM and infrastructure access review | Cloud IAM (GitLab covers code, CI, and registry access only) |
| Vendor and subservice organization monitoring | GRC tooling (GitLab covers the open source slice through the SBOM) |
| Business continuity and disaster recovery testing | DR runbooks and test records |
| Access review sign-off, policy attestation | Your attestation workflow (GitLab supplies the data) |
| The audit itself | A licensed CPA firm |
What this means: GitLab covers the engineering half of the control set, which is the more expensive half to evidence manually. A GRC vendor is still useful, but you can scope it to corporate and HR controls instead of having it screen-scrape your pipelines.
Get started
Framework requirements and controls, the compliance status report, security policies, the security inventory, and most scanners require GitLab Ultimate. Compliance frameworks are available as labels in GitLab Premium, but adherence reporting is not.
To start, apply the SOC 2 framework template to your in-scope projects, then move your scanners into scan execution policies. After that, check the security inventory for gaps before your review window opens.
Try these features with a free trial of GitLab Ultimate.