Shadow factory
Agents borrow personal credentials. No one can verify who or what made a change.
Rules live in each tool, and users decide whether to follow them.
Each agent sees a slice of the lifecycle and retries until it gets it right.
Logs scattered across tools. You can't trace a change from prompt to production.
You see personal tasks and token counts, if anyone tracks them.
Governed factory
Every person and agent has its own identity, so you can audit and revoke it.
One policy plane covers every human and agent, including agents from other vendors.
Agents share lifecycle context, so they spend fewer retries and fewer tokens.
One evidence chain from plan to production.
You see team outcomes and credit spend tied to delivered work.
The foundation of your governed software factory
GitLab Core
The open source foundation under all four layers.
Put agents to work at every stage of the lifecycle, and keep work moving without handoffs.
- Generally available
Duo Agent Platform
Orchestrate agents and flows across every stage of the software lifecycle.
- Generally available
Flows API
Trigger flows from your own scripts and systems.
- Generally available
/goal in Duo CLI
Hand off a whole objective and review the result.
- Coming soon
/goal in chat, your IDE, and Slack
Start and follow tasks end-to-end, from where you already work.
- Beta
Scheduled automations
Set a schedule and let agents handle routine work in the background.
- Generally available
Foundational Flows
Run ready-made, multi-step agent workflows for code review, security analysis, pipeline fixes, and more.
- Generally available
Custom Flows
Build your own multi-step flows to automate your team's processes.
Governance & Security
Find and fix at machine speed.
Stay in control.
Govern every agent
Agents act under a composite identity, limited to the permissions they share with the initiating user.
Agents use only admin-approved tools, models, and MCP servers, and flows run in ephemeral sandboxes with restricted egress.
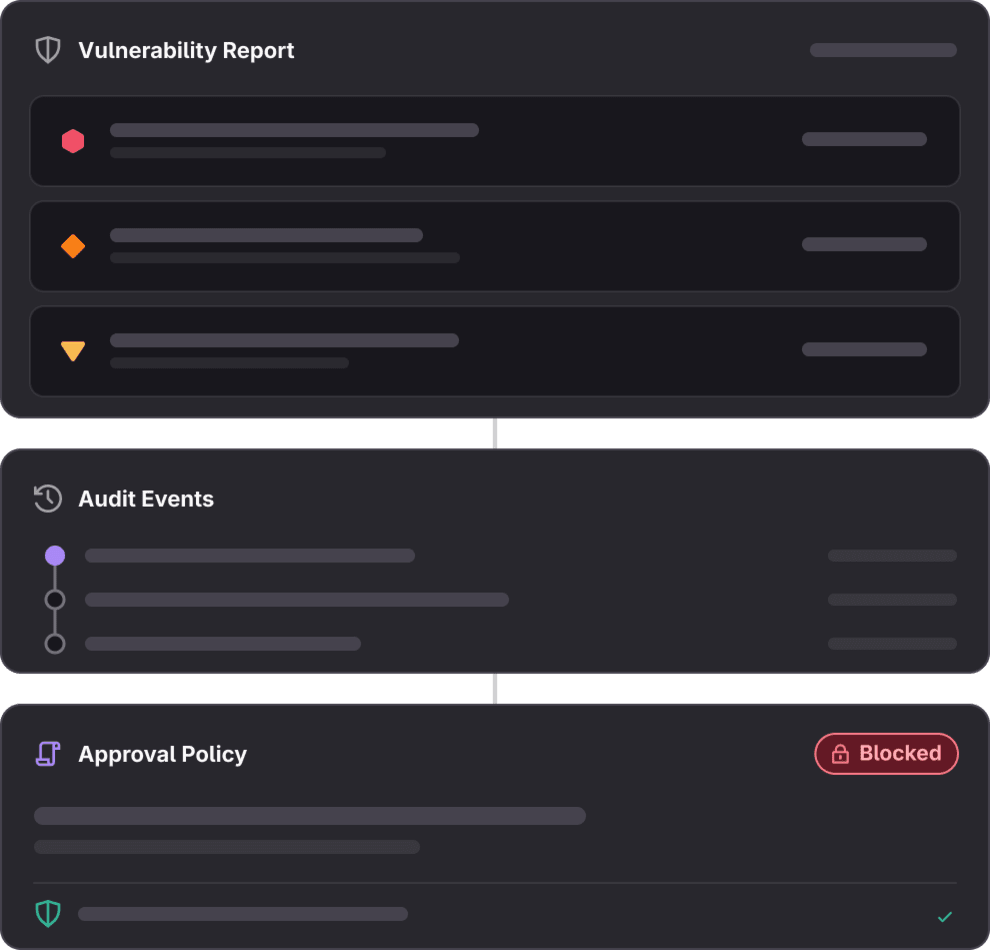
Enforce scans on every change, and hold any with critical or known-exploited vulnerabilities for a designated approver.
Audit every prompt, tool call, and action, attributed to both the agent and the initiating user.
Put security agents to work
Uncover hidden flaws with agentic detection
Hunt business logic flaws with frontier models, including Anthropic's Claude Mythos in eligible environments.
Scan from source to runtime, and track native and third-party findings in one system of record agents can act on.
Resolve findings with agentic remediation
Delegate triage to agents that clear false positives and prioritize real risks.
Review pipeline-verified fixes, each with a rationale and confidence score.
Protect your supply chain
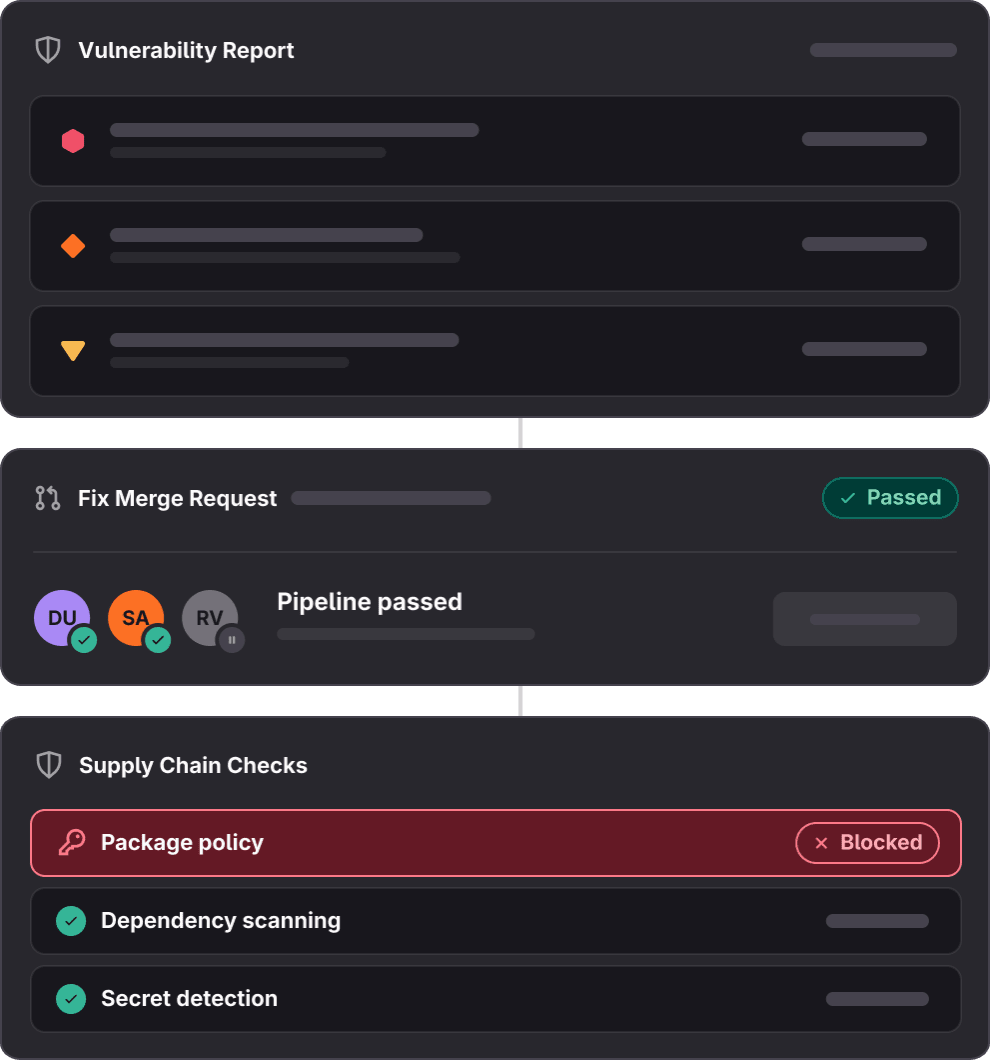
Bump vulnerable dependencies to the nearest safe version and let agents resolve breaking changes.
Replace shared CI/CD variables with scoped credentials from GitLab Secrets Manager, so one compromised job can't expose the rest.
Frequently asked questions
A governed software factory is how agents and people build, secure, and ship software under a consistent set of rules. It brings together agent orchestration, data and context, DevOps infrastructure, and governance and security, so every change, human or agent, runs under your policy and leaves proof of how it got to production.
Automation you can trust, all the way to production.
Put your agents to work under your policy, with proof of every change.