CI/CD
Accelerate CI/CD delivery, with governance built in
Build, test, package, and deploy on one platform, so you can move fast without losing control.
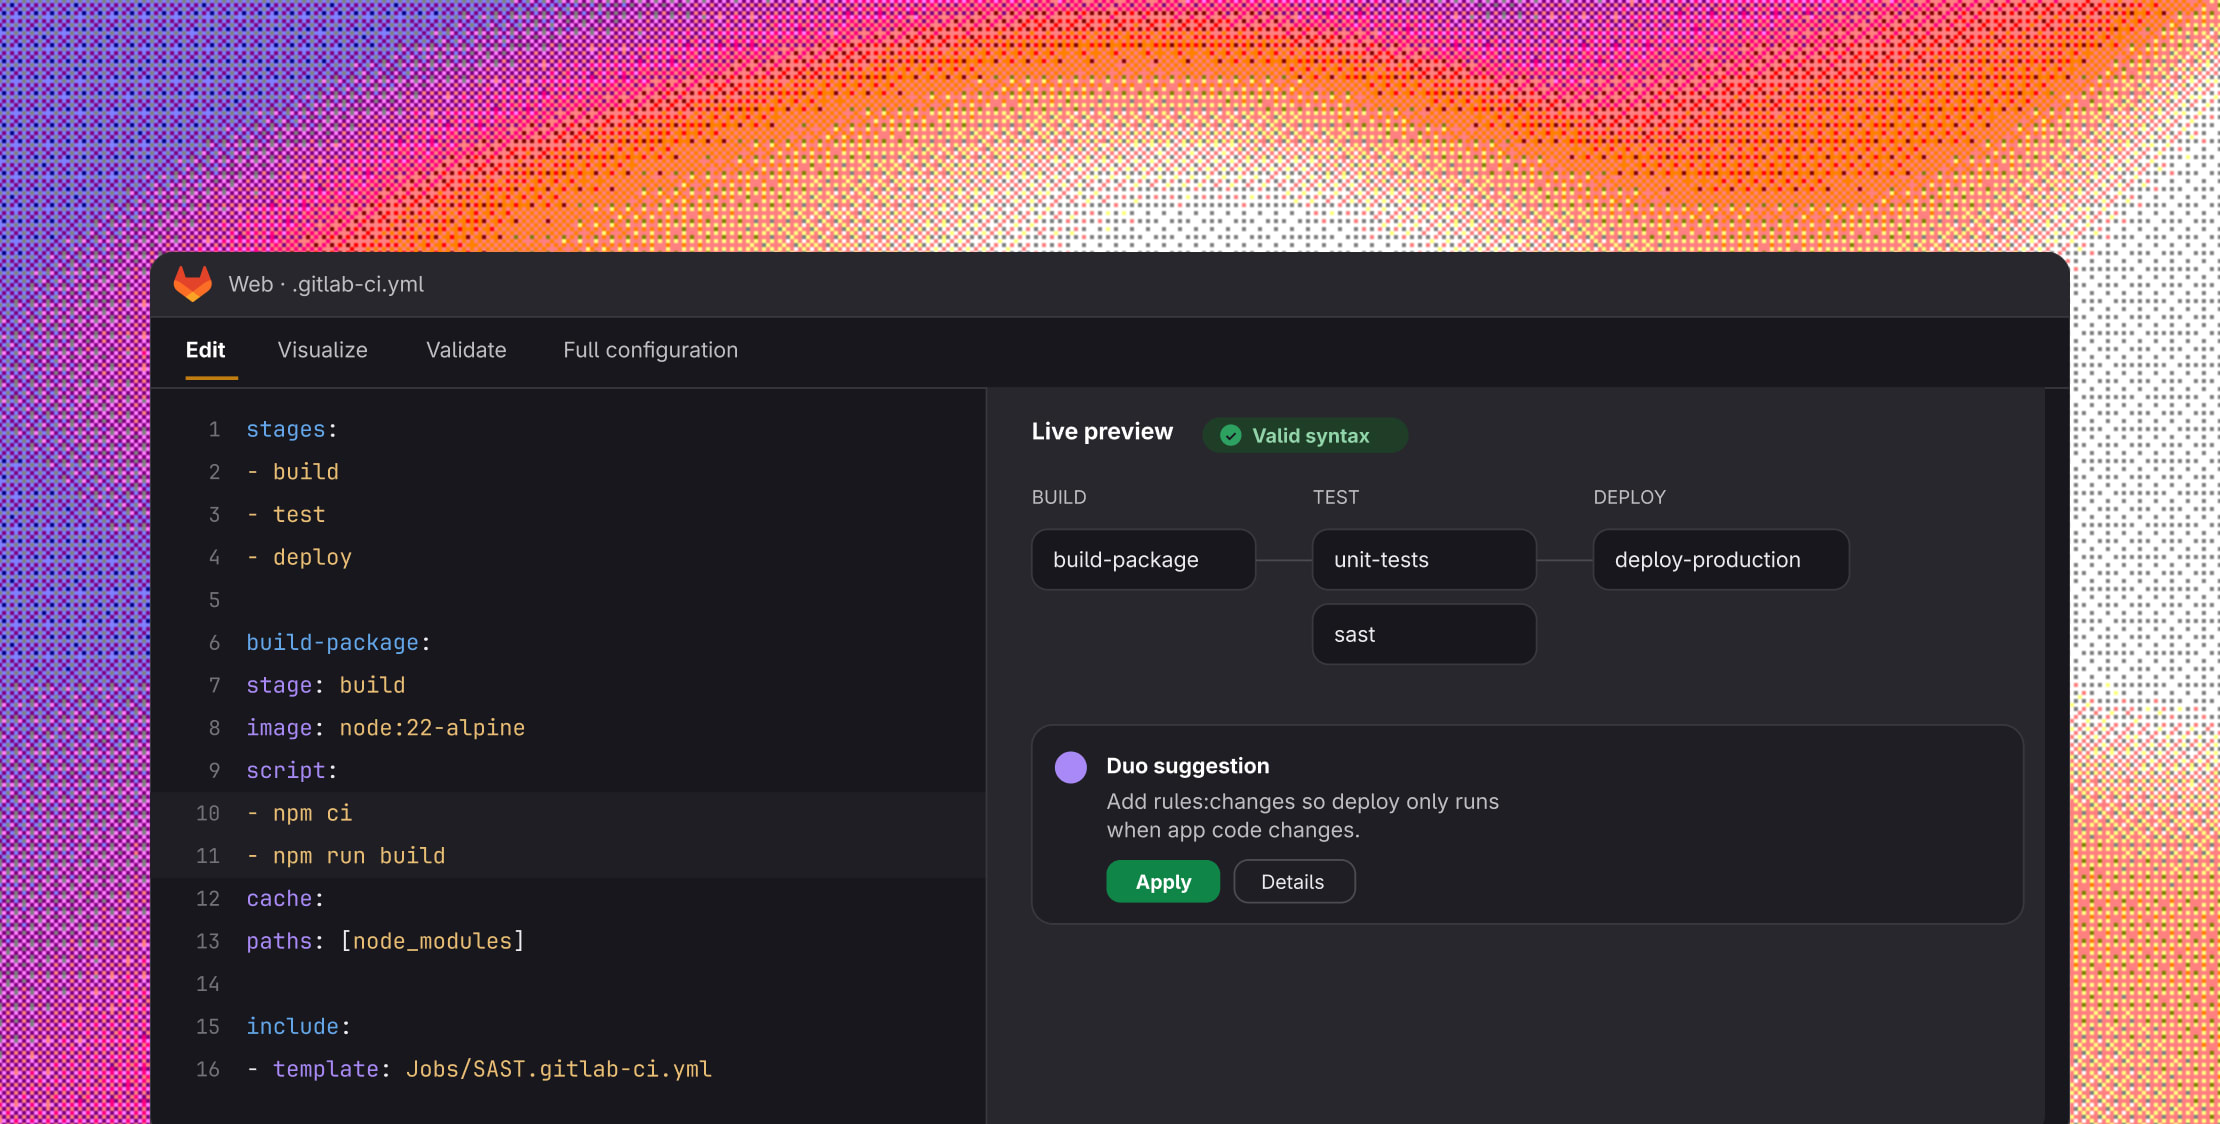
Your pipeline wasn't built for this much traffic
Pipelines built for human-paced commits start to buckle when agents begin pushing code at machine speed.
Coding got faster with AI. If build, test, and deploy don't speed up with it, that gain gets stuck at the commit — not shipped. Automate build, test, package, and deploy from commit to production so the speed you gained in the IDE reaches the finish line.
Learn moreDon't let your pipeline hold you back
Copy-pasted config, a main branch that's never stable, pipelines too slow to give fast feedback — none of that is inevitable or the cost of growing.
Learn how to get started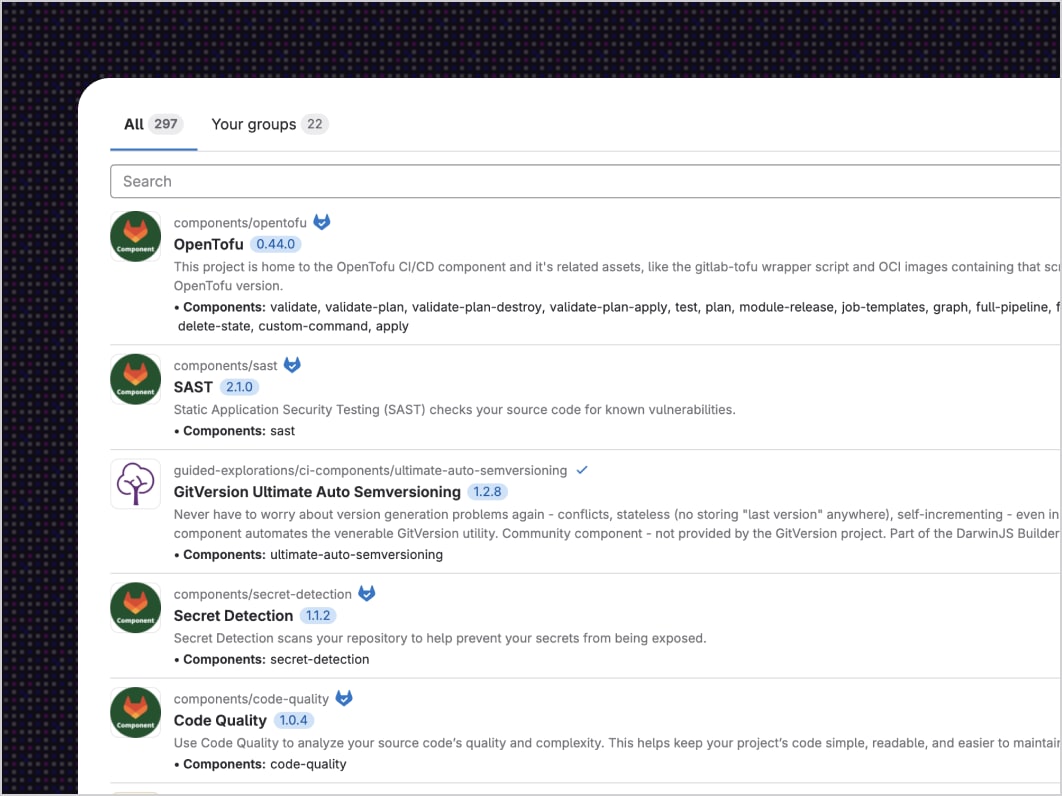
Scale your CI/CD pipelines with:
CI/CD Catalog: No more copy-pasting the same pipeline config into every new project. Publish versioned, reusable components once.
Component Analytics: See how your shared CI/CD components are being adopted, and which projects are running outdated versions.
Merge trains: Stop babysitting a red main branch caused by conflicting merges landing back-to-back.
Parent-child pipelines + DAG execution: Split growing pipelines into independent sub-pipelines so testing starts the moment a dependency finishes.
Cross-project pipelines: Catch a frontend change that breaks the backend before it ships.
Hosted runners: Run CI/CD jobs without provisioning or maintaining your own infrastructure.
Stop discovering security problems after they ship
Catch vulnerabilities and generate compliance evidence while code is still in the pipeline, not when it's a fire drill.
Learn about Security & Compliance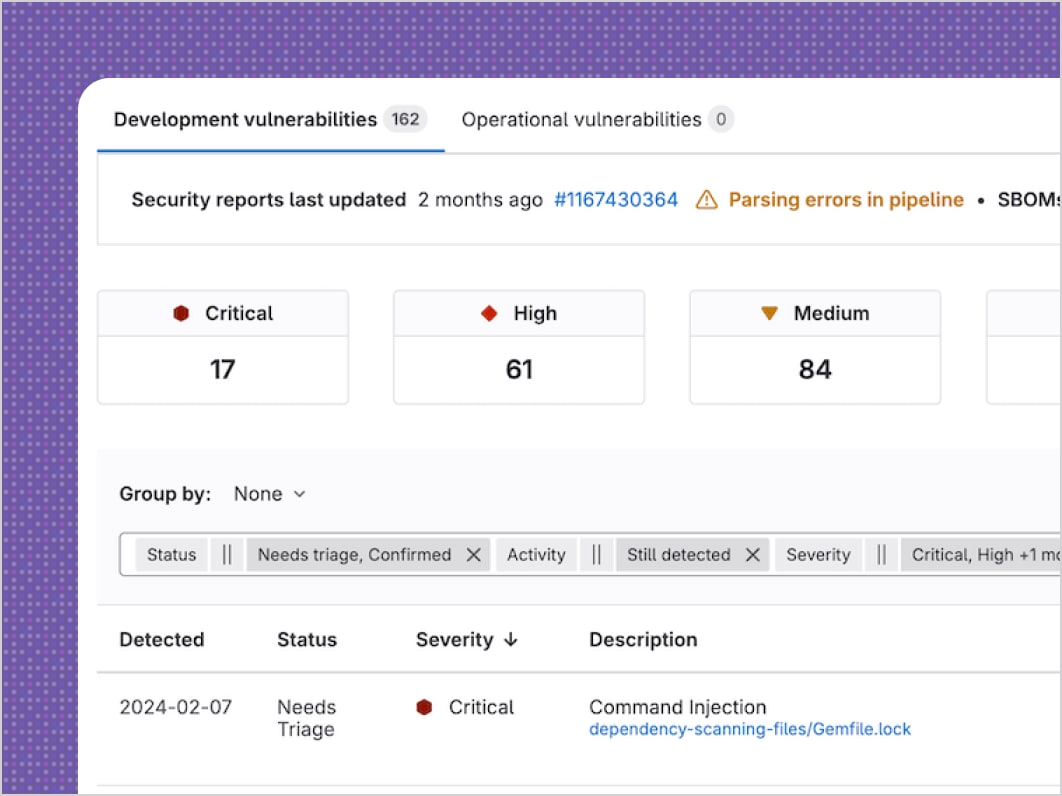
Build security and governance into your pipeline with:
Continuous vulnerability scanning: No more surprise vulnerabilities in a dependency you haven't touched in months.
SAST: Catch vulnerabilities in your own code before deployment, instead of after a customer or auditor finds them.
Pipeline inputs: Close off variable injection by default instead of leaving pipeline customization open to anyone with trigger access.
Compliance pipelines: Skip the tradeoff between speed and compliance: policy enforced as code runs at the same speed as your pipeline.
Deploy without holding your breath
Confidently and consistently release software with enterprise-level delivery tools.
Learn about Enterprise-level deployment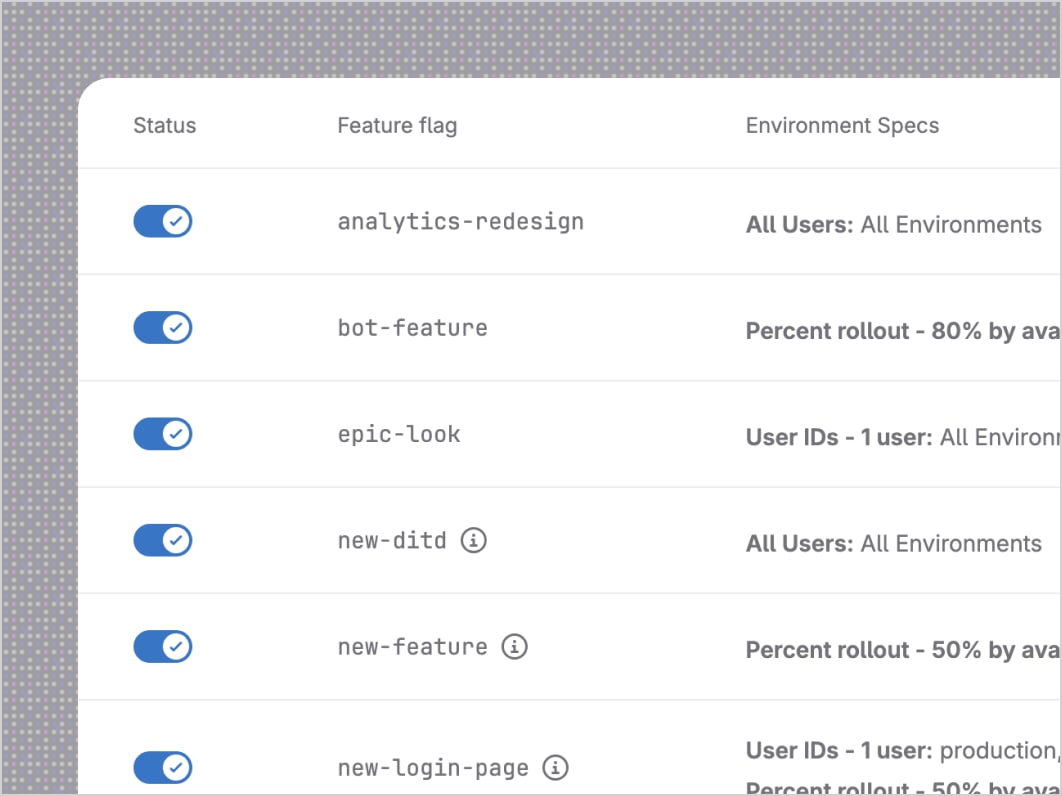
Release your software with:
Progressive delivery: Test in production with a small slice of your user base first.
Canary deployments: Catch problems while the blast radius is small, not after they've reached every user.
Deployment flexibility: Deploy to virtual machines, Kubernetes clusters, or FaaS from multiple cloud vendors, without re-architecting your pipeline for every target.
Stop spending a week auditing what's actually running
Once a component or pipeline template ships, it's easy to lose track of where it's running, which version, and whether it's quietly getting worse. That is, until something breaks and you're auditing repo by repo to find out.
Learn about GitLab DuoGet visibility into your pipelines with:
Component Analytics high-level adoption view: Prioritize maintenance and justify investment by seeing which components are widely adopted vs. abandoned. Learn more.
Component Analytics component usage detail view: Instantly find and fix outdated component versions instead of spending a week auditing manually. Learn more.
Spend less time babysitting pipelines, more time shipping
Offload more with AI that understands your entire software lifecycle.
Learn about GitLab DuoTroubleshoot and automate your pipeline with:
Security vulnerability explanations: Get the explanation, the exploit path, and the fix in one place.
Root cause analysis: Let AI pinpoint why a pipeline failed. No log-diving required.
CI Expert Agent: Generate pipelines that follow your org's standards from the start.
Slide 1 of 4
By switching to GitLab and automating deployment, teams have moved from monthly or weekly deliveries to daily or multiple daily deliveries.
80%
faster CI pipeline builds
90%
less time spent on system maintenance
80%
faster CI pipeline builds
90%
less time spent on system maintenance
Blog
5 ways GitLab pipeline logic solves real engineering problems
Monorepos, microservices, multi-environment deployments, and governance headaches — solved with patterns that compose.
Blog
Track CI component usage across your organization
See whether your shared pipeline standards are actually being followed, without the guesswork.
Video
How Indeed transformed its CI platform with GitLab
See how the world's #1 job site migrated thousands of projects to GitLab CI — and increased productivity and cut costs in the process.